返回科技新闻
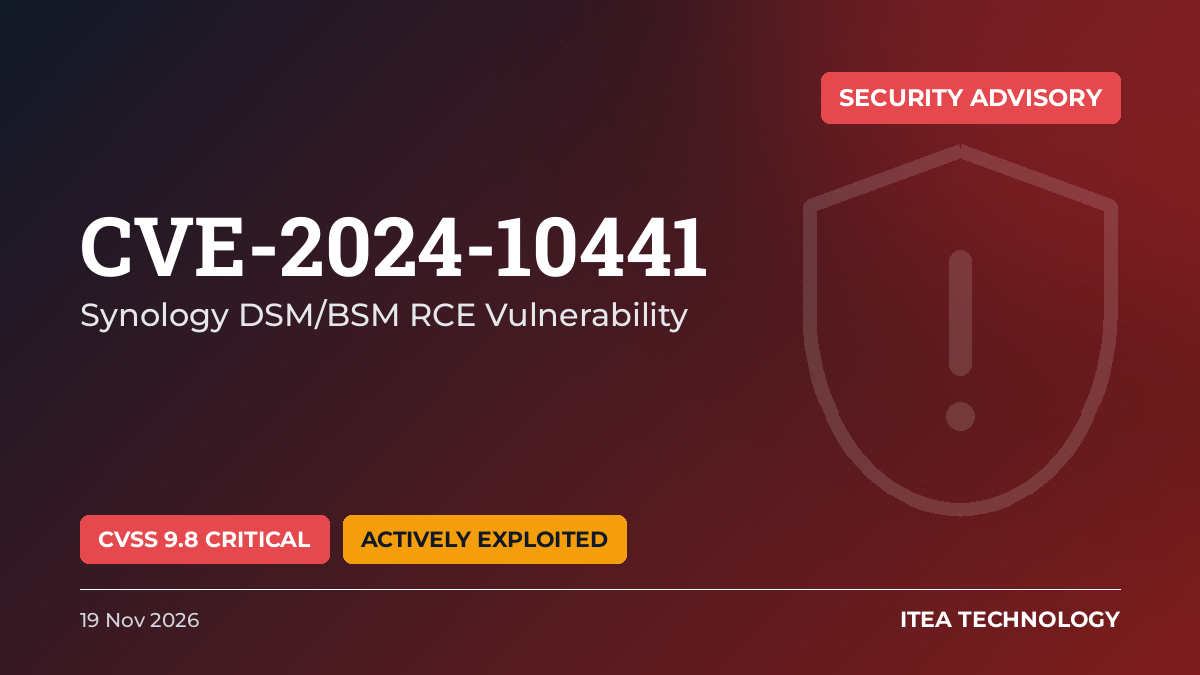
CVSS 9.8 (CRITICAL) · Actively exploited (listed in CISA KEV)
Synology BeeStation OS and DiskStation Manager contain an improper encoding vulnerability in the system plugin daemon. This flaw allows remote attackers to execute arbitrary code without authentication.
Impact
Successful exploitation results in complete system compromise, enabling full control over the affected NAS device.
What to do
Update Synology DSM to version 7.2-64570-4 or later, or BeeStation OS to 1.1-65374 or later immediately.
中文摘要
Synology BeeStation OS 和 DiskStation Manager 的系統外掛程式守護程序存在編碼漏洞。此漏洞允許遠端攻擊者在無需認證的情況下執行任意程式碼。
請立即將 Synology DSM 更新至 7.2-64570-4 或更高版本,或將 BeeStation OS 更新至 1.1-65374 或更高版本。
References
分享: