Back to Tech News
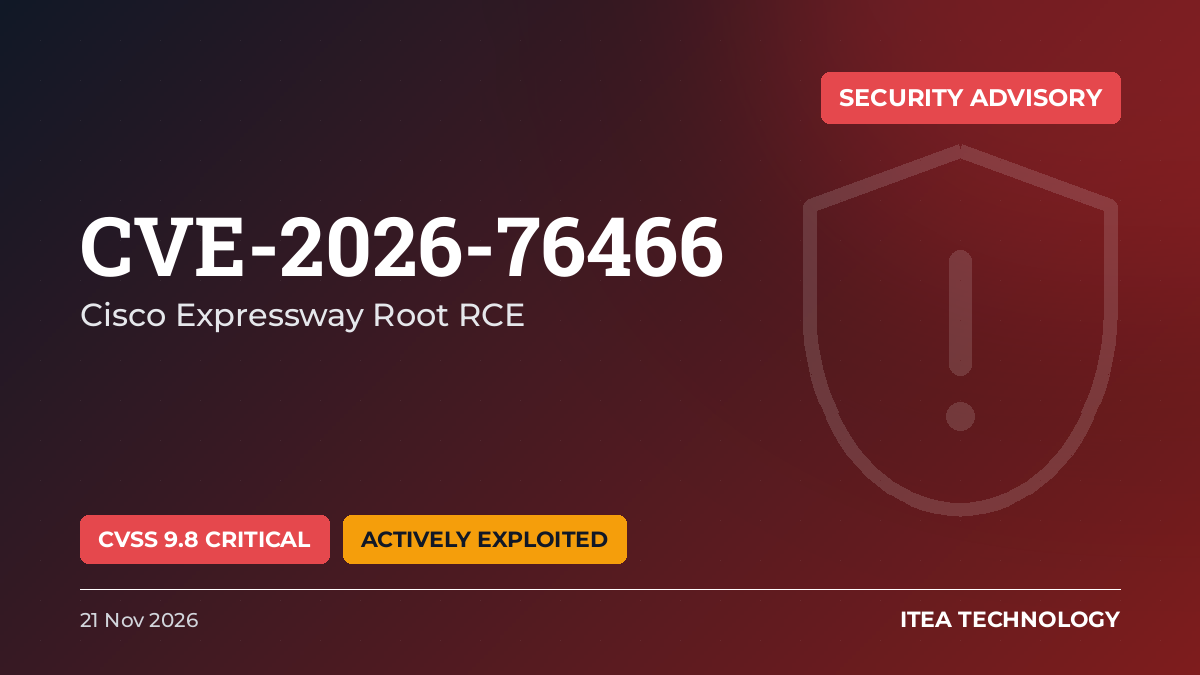
CVSS 9.8 (CRITICAL) · Actively exploited (listed in CISA KEV)
Cisco Expressway Series devices contain a critical vulnerability allowing unauthenticated remote attackers to execute arbitrary OS commands as root. The flaw stems from persistent cookies and insufficient client certificate validation in the database service.
Impact
Successful exploitation grants full root access to the underlying operating system, compromising confidentiality, integrity, and availability.
What to do
Apply vendor patches immediately and follow CISA BOD 26-04 guidance. Discontinue use if mitigations are unavailable.
中文摘要
Cisco Expressway 系列設備存在嚴重漏洞,允許未經認證的遠端攻擊者以 root 權限執行任意作業系統命令。此缺陷源於資料庫服務中的持久性 Cookie 及客戶端憑證驗證不足。
立即套用廠商修補程式並遵循 CISA BOD 26-04 指引。若無法緩解則停止使用該產品。
References
Share: